Tamper-evident photos, as an API.
One call opens a camera page in your app. Your users shoot, we seal, anyone can verify with a link. No SDK. No storage. No crypto to build.
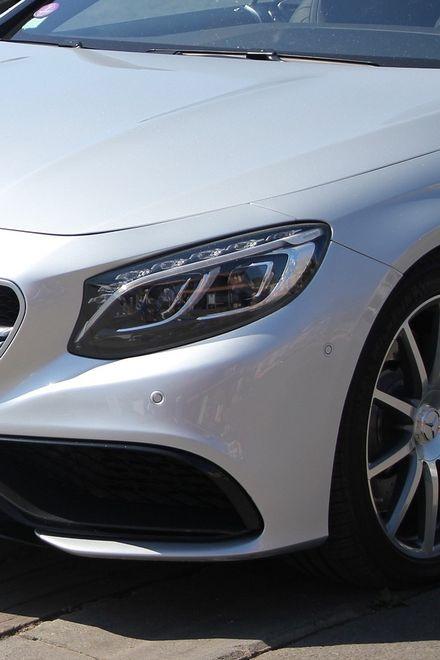 Front · live capture
- eIDASqualified timestamp
- C2PAconformant for photos
- RFC 3161timestamp protocol
- Open sourceverifier
Photos on your servers are your word against theirs.
Any photo can be passed off
From the gallery, another day, or an editor.
↓ Live capture at pickup and returnYou hold the files
So the side that loses says you changed them.
↓ Sealed by a neutral third partyNobody else can check
The other party, an insurer or an expert has to take your word.
↓ Verifiable by anyone, without you or us
You can build the hashing. You can't build the third party.
A timestamp alone isn't a proof. You'd still need live capture, C2PA signing, storage and a page anyone can check. tryVidimus does all of it in one API.
tryVidimus seals the photos instead of your platform. It works like an e-signature API: create a session, send the link, get a webhook, share a proof anyone can verify. We certify; we never arbitrate.
- 1Create an account
- 2Scan the QR with your phone
- 3Open your first proof
$ curl -X POST https://api.tryvidimus.com/v1/capture-sessions \
  -H "Authorization: Bearer $TRYVIDIMUS_API_KEY" \
  -H "Content-Type: application/json" \
  -H "Idempotency-Key: $(uuidgen)" \
  -d '{"external_reference":"booking_4471","party":"provider","stage":"pickup"}'
← 201 { "capture_url": "https://api.tryvidimus.com/v1/capture-sessions/…",
        "expires_at": "2026-09-28T18:30:00Z" }
→ webhook proof.sealed  prf_018f2e4a · booking_4471
Why it holds up
Live capture at pickup and return
No app to install, no gallery uploads.
One call returns a capture link. The person at the handover opens it in their phone's browser and takes the shots you asked for, in your colors. Link the return to the pickup: each is sealed, and one points to the other.
- Front
- Driver side
- Odometer
- Gallery import: off
Sealed by a neutral third party
The files never touch your servers.
Every photo is fingerprinted (SHA-256) and signed (C2PA). Each proof gets an eIDAS qualified timestamp from Certigna, usually within seconds. Originals are kept for 24 months.
- Fingerprint
- sha256 9f2c…e41a
- C2PA signature
- Signed
- Certified time
- Certigna · eIDAS qualified
Verifiable by anyone, without you or us
Send a link instead of arguing.
Each proof has a public page: no account, no access to your back office, the certified time next to the observed time, and what the proof does and does not show. The verifier is open source.
$ curl -s https://api.tryvidimus.com/v1/public/proofs/prf_…/bundle \
    | jq -r .timestamp.tsr_base64 | base64 -d > token.tsr
$ openssl ts -verify -digest <manifest_sha256> -in token.tsr -CAfile chain.pem
Verification: OK
Open-source verifier →Ships like the APIs you already use
A trusted third party, without the sales contract, the certificates or the demo.
A full test mode for free. Signed webhooks you can resend and test. OpenAPI, a TypeScript client, a CLI and an MCP server for your coding agent. €1 per sealed proof. No subscription, no sales call.
POST https://your-app.example/webhooks
x-signature: t=1759655652,v1=5f1c…a9e2

{
  "event": "proof.sealed",
  "proof_id": "prf_…",
  "external_reference": "booking_4471",
  "stage": "pickup",
  "status": "sealed"
}
Developers →
Don't trust us. Verify.
Check any proof with the open-source verifier, and watch our status page. That's the whole point of a third party.
Questions developers ask
- What is a proof legally worth?
- Each proof carries an eIDAS qualified timestamp (article 41 of the regulation): in the EU, the date and the integrity of the sealed data are presumed accurate, until proven otherwise. A proof does not show that the scene is genuine, or who took the photos.eIDAS and C2PA, explained →
- Who does what?
- Certigna, a qualified trust service provider, certifies the time: one qualified timestamp per proof. tryVidimus runs the capture, fingerprints the photos, signs them (C2PA) and keeps the files. Anyone can verify a proof, with our public page or without us, using the open-source verifier.
- Why not build it ourselves?
- You can code the hashing. But a proof you seal yourself is still your word: the other side can say you changed it. What you cannot build is the neutral third party.
- What if tryVidimus disappears?
- Download the signed copy of each photo and the verification bundle of the proof (fingerprints, manifest and RFC 3161 timestamp token). The open-source verifier and openssl check them without our servers. Originals stay with us for 24 months.
- Where are photos stored?
- Files are stored with Cloudflare (R2). The database is hosted by Supabase in Frankfurt (EU), the API and customer area servers by Elestio, and the signing keys by Amazon Web Services (KMS, Paris, EU). Some providers, Cloudflare among them, can access data from outside the EU: these transfers are covered by the European Commission's standard contractual clauses or by the EU-US Data Privacy Framework.Privacy policy →
- Do you build the dispute file?
- No. We seal, you compose: list a transaction's proofs by external_reference and download each proof's verification bundle.Compose a dispute file with the API →
- Does the person taking photos need an app or an account?
- No. The capture is a web page that opens in their phone's browser.
- Does it work inside my native app?
- Yes, in a web view: there is no native SDK. The Mobile apps guide gives the iOS and Android settings.Mobile apps guide →
- Can users upload photos from their gallery?
- No. Photos are taken in the capture flow; importing from the gallery isn't offered.
- Do you decide who's right?
- No. We certify; we never arbitrate. There is no automatic comparison: the decision stays with you, your users or their insurer.
- Is the test mode the real thing?
- Yes: the full API, except the timestamp, which is simulated and has no legal value. Test files are deleted after 48 hours.